As cybersecurity threats continue to rise and regulatory requirements tighten, organizations supporting government contractors must ensure they meet stringent security standards. CMMC compliance for MSPs is becoming essential to strengthen security and protect sensitive data. At Boston Managed IT, we are taking proactive steps to align with the Cybersecurity Maturity Model Certification (CMMC) framework to enhance our security posture and support our clients in meeting compliance requirements.
Why CMMC Compliance Matters for MSPs
The Department of Defense (DoD) introduced CMMC to protect Controlled Unclassified Information (CUI) and Federal Contract Information (FCI) within the defense industrial base. While Boston Managed IT does not handle CUI, aligning with CMMC compliance for MSPs reinforces our commitment to cybersecurity and enables us to better support clients who require compliance with federal security standards.
By implementing CMMC-aligned security measures, we are:
- Strengthening our own cybersecurity framework to prevent threats and mitigate risks.
- Ensuring that our services do not introduce vulnerabilities to our clients’ compliance efforts.
- Preparing for future regulatory changes that may impact MSPs and IT service providers.
Steps We Are Taking to Align with CMMC Compliance
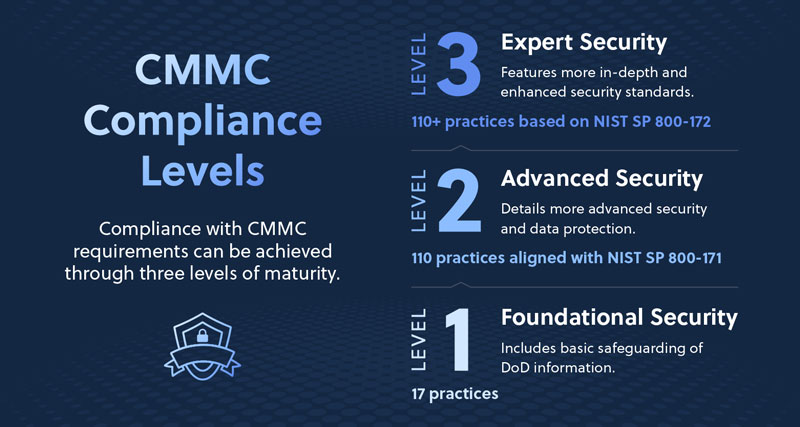
Boston Managed IT is implementing a structured plan to align with CMMC Level 1 and Level 2 security controls, which focus on fundamental cyber hygiene and NIST SP 800-171 compliance. Our approach includes:
1. Enhancing Access Control & Authentication
- Implementing Multi-Factor Authentication (MFA) across all systems.
- Enforcing Role-Based Access Control (RBAC) to limit access based on job functions.
2. Strengthening System & Network Security
- Deploying Endpoint Detection & Response (EDR) solutions for real-time threat detection.
- Enhancing firewall security and intrusion detection capabilities.
3. Developing Comprehensive Security Policies
- Establishing a Written Information Security Program (WISP) that documents our security measures.
- Implementing an Incident Response Plan (IRP) to ensure a rapid response to potential security incidents.
4. Conducting Employee Security Awareness Training
- Rolling out cybersecurity awareness training and phishing simulations to educate employees on best practices.
- Providing guidelines for secure data handling and access management.
5. Monitoring & Continuous Improvement
- Deploying Security Information and Event Management (SIEM) solutions for centralized logging and threat monitoring.
- Conducting regular security audits and risk assessments to identify and address potential vulnerabilities.
How This Benefits Our Clients
By aligning with CMMC compliance for MSPs, Boston Managed IT ensures that our clients—especially those working with the DoD—can trust that their IT infrastructure is secured against cyber threats. Our proactive approach reduces the compliance burden on our clients and provides them with a secure foundation for their business operations.
FAQs About CMMC Compliance for MSPs
1. Do MSPs need to be CMMC certified?
No, MSPs do not need CMMC certification unless they handle CUI directly. However, aligning with CMMC security standards enhances your credibility and supports your clients in meeting compliance.
2. What level of CMMC should an MSP align with?
MSPs should aim to meet CMMC Level 1 or Level 2 security controls, which focus on basic cyber hygiene and NIST SP 800-171 requirements.
3. How can MSPs help clients with CMMC compliance?
MSPs can assist clients by implementing strong security controls, access management, SIEM solutions, and incident response plans to align with CMMC requirements.
Looking Ahead
While we are not seeking formal CMMC certification at this time, we recognize that the landscape of cybersecurity compliance is constantly evolving. By aligning with these security standards today, we are positioning ourselves and our clients for long-term success in an increasingly regulated environment.
Boston Managed IT remains committed to delivering secure, high-quality IT services. If you have any questions about how our security initiatives can support your business’s compliance needs, reach out to us today!